
AI Governance for the Enterprise: Building Trust, Control, and Accountability at Scale
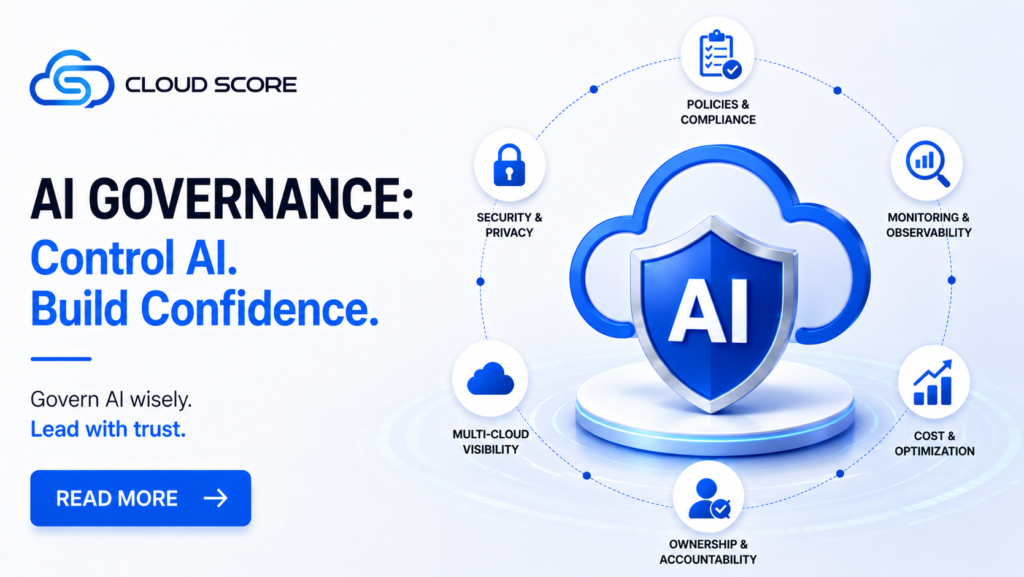
AI Governance is becoming essential as artificial intelligence moves from experimentation into everyday enterprise operations. Organizations are using AI to automate business processes, assist employees, analyze large volumes of data, generate content, support software development, improve customer experiences, and make faster decisions. Generative AI and AI agents are accelerating this transformation even further. But as AI becomes more deeply connected to enterprise applications, cloud infrastructure, business data, and operational workflows, organizations face a critical challenge: How do enterprises scale AI without losing visibility, security, accountability, or control? That is where AI Governance becomes essential. AI Governance provides enterprises with a structured framework for managing how artificial intelligence is developed, deployed, accessed, monitored, secured, governed, and optimized throughout its lifecycle. The objective is not to restrict AI innovation. The objective is to create an environment where enterprises can adopt AI confidently, responsibly, securely, and at scale. What Is AI Governance? AI Governance is the framework of policies, processes, controls, technologies, and responsibilities used to manage artificial intelligence throughout its lifecycle. A practical AI Governance framework helps organizations answer fundamental questions such as: What AI systems are being used? Which AI models are approved? Where are AI applications deployed? Who owns each AI workload? What enterprise data can AI access? Which users and applications can access AI services? Are AI systems operating according to organizational policies? How are AI risks identified and managed? How much do AI workloads cost? Are AI services performing reliably? Can AI-related decisions and actions be audited? Without this visibility, AI adoption can quickly become difficult to manage. Why Do Enterprises Need AI Governance Now? Enterprise AI adoption is happening faster than traditional governance processes were designed to handle. A few years ago, AI initiatives were often limited to specialized data science teams. Today, AI can be introduced almost anywhere. Developers can integrate an LLM through an API. Business teams can adopt AI-powered SaaS applications. Engineering teams can deploy AI agents. Employees can use generative AI assistants. Organizations can build AI applications using multiple model providers and cloud platforms. This creates a highly distributed AI ecosystem. An enterprise may soon have hundreds of AI-enabled applications, models, APIs, agents, datasets, and infrastructure components operating simultaneously. Without effective AI Governance, organizations can lose visibility into: What AI exists, who is using it, what it can access, what it costs, and what risks it introduces. The New Enterprise AI Governance Challenge AI introduces challenges that extend beyond the AI model itself. Consider a typical enterprise AI application. It may involve: Users ↓ Applications ↓ AI Agents ↓ LLMs / AI Models ↓ APIs ↓ Enterprise Data ↓ Databases ↓ Cloud Infrastructure ↓ Networks, Compute, Storage and Security Controls Each layer introduces its own risks and operational dependencies. An AI application may be secure at the model layer but expose sensitive information through an improperly configured API. An AI workload may work correctly but generate unexpectedly high cloud or inference costs. An AI agent may have excessive permissions. A model may depend on an infrastructure service experiencing performance degradation. This is why Enterprise AI Governance must look beyond individual models. It must consider the complete AI ecosystem, including applications, models, agents, data, APIs, infrastructure, security, cost, and operational dependencies. What Are the Core Pillars of Enterprise AI Governance? A strong AI Governance framework should address several interconnected areas. AI Visibility Enterprises cannot govern what they cannot see. Organizations need an inventory of their AI ecosystem, including: AI applications AI models AI agents APIs Data sources Cloud services Infrastructure Model providers Owners Business functions Visibility creates the foundation for every other governance capability. The first question of AI Governance should therefore be: What AI are we currently using? AI Ownership and Accountability Every enterprise AI system should have clear ownership. Organizations should understand: Who owns the AI application? Which business unit uses it? Who is responsible for the model? Who owns the underlying infrastructure? Who approves access? Who responds when something goes wrong? Clear ownership prevents AI systems from becoming unmanaged technology assets. It also ensures that accountability exists throughout the AI lifecycle. Data Governance and Privacy AI systems often depend heavily on enterprise data. That data may include: Customer information Financial records Employee information Intellectual property Operational data Source code Documents Internal communications AI Governance should define what information AI systems are allowed to access and how that information can be processed. Organizations need controls around: Data classification Data access Data residency Sensitive information Retention Model training Prompt data AI-generated output The fundamental principle should be: AI should only access the data required for its intended business purpose. AI Security AI systems introduce new attack surfaces alongside traditional cloud and application security risks. Enterprises need security controls across: Identity Access permissions Models APIs Applications AI agents Infrastructure Networks Data AI agents require particular attention because they may be capable of interacting with enterprise systems or automatically performing actions. AI Governance should ensure that AI receives: The right access, to the right resources, for the right purpose, under the right controls. AI Risk Management Not every AI application carries the same level of risk. For example, an internal meeting-summary assistant may have relatively limited business impact. An AI system supporting decisions within a critical financial or healthcare process may require substantially greater oversight. Organizations should therefore classify AI systems according to factors such as: Business impact Data sensitivity User exposure Autonomy Decision-making capability Regulatory requirements Infrastructure dependency Financial exposure This allows enterprises to apply stronger governance controls to higher-risk AI workloads. A risk-based AI Governance strategy ensures that governance effort is aligned with the potential impact of each AI system. AI Model Governance Enterprises may eventually use dozens or even hundreds of AI models. These models may come from different providers and serve different purposes. Organizations need visibility into: Which models are being used Why each model was selected Model versions Model ownership Performance Accuracy Cost Usage Approved use cases Data access Model governance becomes particularly important as organizations begin dynamically selecting